Comparison · 7 November 2026 · 5 minute read
Visitor identification and GDPR: providers compared
Cookie, consent, IP address, server location and certifications at Leadfeeder, SalesViewer, Leadinfo and more, according to the providers, with sources.
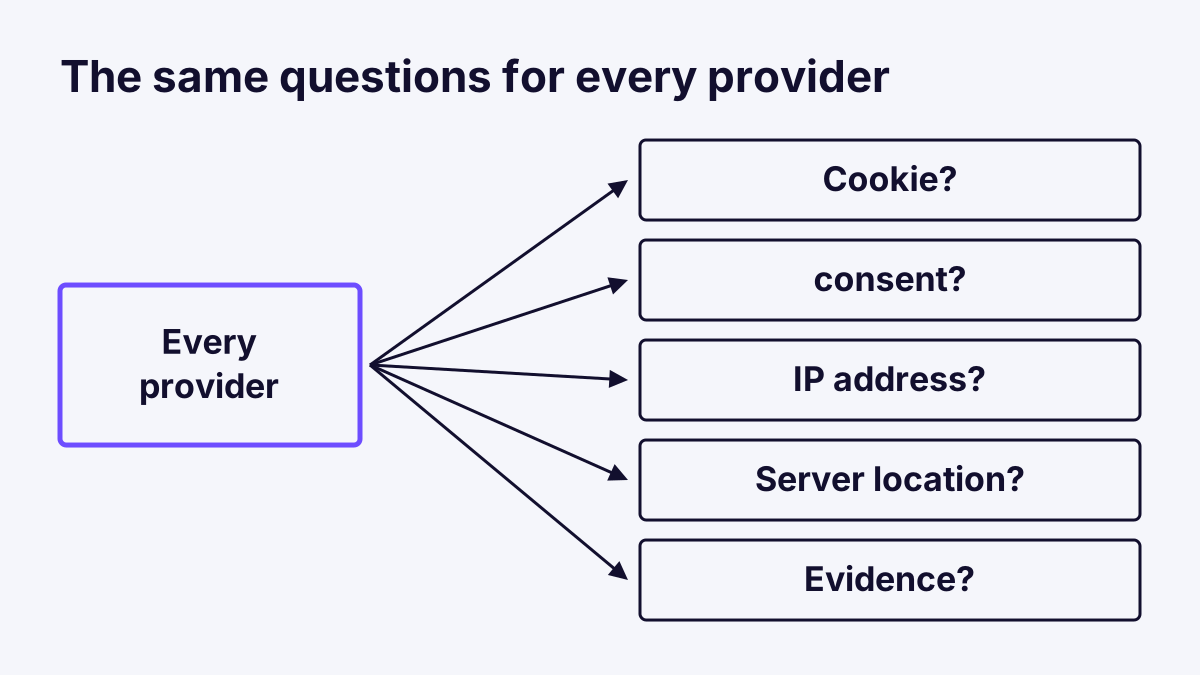
Anyone who uses visitor identification must be able to explain to the data protection officer or the boss what the tool does with data. The providers describe this very differently. This article compiles what eight providers say on their own pages about cookie, consent, IP address, server location and certifications. These are statements by the providers, not an assessment and not a verdict on lawfulness. The article is not legal advice. The legal classification is in Visitor identification and GDPR: a sober assessment.
The statements at a glance
All pages retrieved on 7 November 2026. „Not stated“ means: the page checked says nothing on this.
| Provider | Cookie | Consent according to the provider | IP address | Server location | Evidence |
|---|---|---|---|---|---|
| Leadfeeder | Page refers to cookie pages | Page does not explain the consent mode | not stated | AWS in EU/EEA, location not named | ISO 27701 mentioned, ISO 27001 as basis |
| SalesViewer | „cookie-free tracking“ | not addressed, opt-out named as a technical measure | „no IP tracking“, without explanation | „German infrastructure“, location not named | not stated |
| Leadinfo | two first-party cookies, optional, cookie-free also possible | Consent is recommended, the customer chooses the legal basis | counts as personal data, deletion concept | Ireland (AWS) | ISO 27001 mentioned, page inconsistent |
| Albacross | yes, cookies are set and read | requires valid consent | can be personal data | not stated | not stated |
| Snitcher | first-party cookie, no third-party cookies | Documentation recommends calling the person matching only after consent | not stated | not stated | not stated |
| RB2B | not stated | for company identification a consent solution is mandatory | EU and UK IPs only to trigger the script | not stated | not stated |
| HubSpot | Tracking code captures activity and identifiers | Banner „may be necessary“ | is captured | not stated on the help page | not stated on the help page |
| Whovisit | no cookie | Script loads only after consent | is discarded after assignment | Netherlands | not stated |
The sources in detail: Leadfeeder security, SalesViewer data protection, Leadinfo GDPR, Albacross and GDPR, Snitcher documentation, RB2B GDPR, HubSpot Buyer Intent.
What stands out
The legal basis is distributed differently. Leadinfo lets the customer choose between consent and legitimate interest and recommends asking for consent before activating the code. Albacross requires consent for the cookies. RB2B prescribes a consent solution for company identification. With SalesViewer, the page checked names neither consent nor legal basis. The question of when which basis holds is addressed in Consent or legitimate interest: how to decide.
Cookie does not automatically mean consent. No cookie does not automatically mean none. In Germany, § 25 TDDDG (the German Telecommunications Digital Services Data Protection Act) decides whether the end device is accessed, and the GDPR decides on the processing itself. The two are checked separately, see Section 25 TDDDG: cookies and tracking in Germany. A provider without a cookie can still process data, and a provider with a cookie can have consent obtained.
There are two readings on the IP address. Leadinfo and Albacross treat the IP address as possibly or actually personal data. SalesViewer writes „no IP tracking“ without explaining how the IP is handled. Why the question is not easy to answer is explained in IP address and GDPR: is it personal data?.
Certifications are hard to compare. Leadfeeder names ISO 27701 and lists the documents on a subpage. Leadinfo names ISO 27001 but elsewhere on the same page has „aims for“, which merits follow-up questions. For Albacross, Snitcher and RB2B, the pages checked list no standards. A seal does not replace a contract. Ask for the certificate itself and check its validity and scope.
Server location. Only Leadinfo names a country (Ireland). Leadfeeder names the EU and the European Economic Area, SalesViewer „German infrastructure“. Anyone who needs the exact location asks for it in the data processing agreement.
What you should ask every provider for
- The data processing agreement and the list of subprocessors. The checklist is in Data processing agreement: checklist for web tools.
- A written description of which data is stored and for how long.
- A statement on what happens with missing consent: does the script not load at all, or does partial identification continue?
- The evidence for standards, not just the logo.
Frequently asked questions
Is Leadfeeder compatible with the GDPR? This question cannot be answered in general, either for Leadfeeder or for other providers. What matters is how you use the tool: consent, contract, information in the privacy policy. What the provider itself states is in the table above.
Is it enough if a provider is cookie-free? Not on its own. Even without a cookie, traffic is processed. Also check IP handling, storage period and legal basis.
Which documents do I need before starting? At the least the data processing agreement, a paragraph in the privacy policy and a consent solution that releases the script only after approval. How to set up the banner is shown in Setting up the cookie banner: asking for analytics consent properly.